Security assessment
A clear picture of your organization's security: access, backups, devices, practices and the most important risks. You get a simple report with prioritized actions that fit your means.
Learn more
YottaSec Haïti
YottaSec Haïti is an information security consulting firm, registered in Haiti with the Ministry of Commerce and Industry. Our mission: to give Haitian organizations, including small and medium-sized ones, accessible security advice that fits their reality.
Our approach is proactive: prevent, detect and respond. It rests on six services: the security assessment, the vCISO (virtual CISO), independent IT consulting, staff awareness training, penetration testing and incident response, to build lasting cyber resilience.
Led by Blaise Arbouet, certified CISSP, C‑CISO and ISO 27001 Lead Implementer, the firm offers independent advice: we do not resell any product. Our ambition is to help build a safer and more resilient digital environment in Haiti.
Six complementary services, offered independently and adapted to the reality of Haitian organizations.
A clear picture of your organization's security: access, backups, devices, practices and the most important risks. You get a simple report with prioritized actions that fit your means.
Learn more
A part-time security leader: risk assessment, security roadmap, policies and support for your management, without the cost of a full-time position.
Learn more
Neutral advice on your technology strategy, infrastructure and vendors. We do not resell any product and do not carry out the fixes, which keeps our recommendations objective.
Learn more
Practical sessions on the most common traps: fraudulent emails, passwords, personal devices, information sharing. No jargon, with examples drawn from situations your teams know.
Learn more
We test your networks, applications and cloud environments the way a real attacker would, then give you a prioritized list of what to fix first.
Learn more
When a breach or ransomware attack occurs, we help you contain it, investigate what happened and restore your operations, with clear communication at every step.
Learn moreA simple, transparent process, from the first conversation to the follow-up on the fixes.
We listen to your context: what you need to protect, your constraints and your priorities. A free consultation, no obligation.
We carry out the agreed assessment or tests, within a clear scope defined with you at the start.
You receive a clear report: an executive summary, the technical detail and actions ranked by priority.
We present the results to your team and remain available to answer questions while the fixes are made.
We work with organizations in every sector, in particular those that attackers target first.
These sectors are described based on general trends observed in the region and worldwide. Every engagement starts with an analysis of your actual situation.
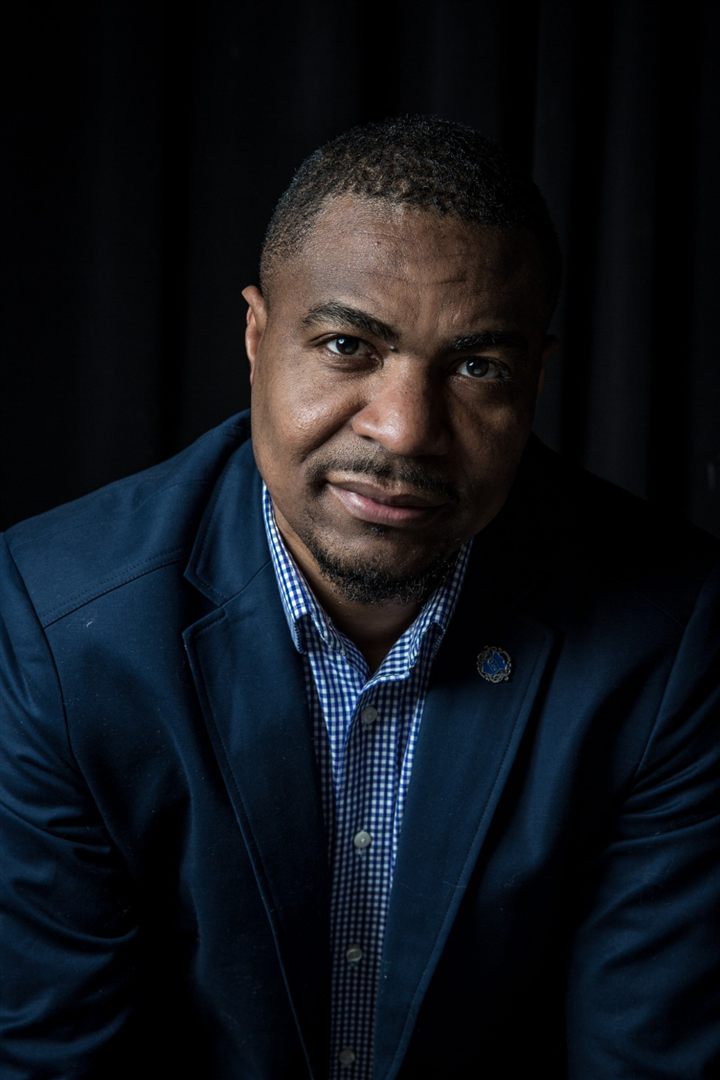
Leading YottaSec Haïti
Founder · CISSP · C‑CISO · ISO 27001 LI
Blaise Arbouet has more than 25 years of experience in information technology and information security. He holds the CISSP, C‑CISO and ISO 27001 Lead Implementer certifications and a graduate degree in IT governance, audit and security from the Université de Sherbrooke.
An entrepreneur, co-founder of Tainos CyberCon, teacher and speaker, he wants to see Haiti adopt ICT as an engine of economic development while protecting its critical infrastructure.
It is a free call or meeting, with no obligation. We learn about your context, what you want to protect and the kind of help you need. We then send you a written proposal with the scope and deliverables.
Yes, the first consultation is free and with no obligation. The security assessment, on the other hand, is a fixed-price service: the price and deliverables are set out in the written proposal, before you commit.
Yes. We treat all client information as confidential and can sign a non-disclosure agreement before an engagement begins.
Organizations in all sectors, in particular banks and financial institutions, telecommunications, public institutions, NGOs, healthcare, education and growing businesses. Each engagement is adapted to the size and means of the organization.
It depends on the scope: a few days for a targeted test, longer for ongoing support such as a vCISO. The duration is set out in the proposal, before you commit.
No, deliberately. Our advisory and assessment services are independent: we do not resell any product and do not carry out the fixes. You can give them to your own team or your vendors, and we can verify the result.
A free consultation, no obligation, to understand your situation.